When evaluating the sheer amount of bitcoin lost, the recent exploits of the Coldcard hardware wallet and the Liquid Network sidechain do not rank as the most serious security incidents in the history of crypto. However, they represent a far more dangerous development than the relatively common exchange hacks of the past.
In previous crypto disasters, the faithful could point to viable excuses involving user error, such as the use of centralized, unregulated exchanges or interacting with complex smart contracts that could be buggy and lead to a loss of funds. For example, many feared that the Mt. Gox hack and subsequent bankruptcy in early 2014 would destroy the nascent financial technology, and a similar phenomenon occurred with the collapse of FTX roughly eight years after that. But these exchanges have since been replaced with more serious, regulated options, ultimately culminating in the approval and launch of bitcoin exchange-traded funds (ETFs) from the likes of BlackRock and Fidelity.
With respect, I don’t think “not your keys, not your coins” has quite the same ring after we have recently discovered, “yes your keys, not your coins”
— Star Heartsong · $ASST ALL-IN⛳ · WAGMI 😜🏆✝️🔥🕊️ (@DrStarHeartsong) September 10, 2026
That said, these more recent security failures did not occur on completely centralized, custodial platforms where a hardcore bitcoin believer could easily chime in with, “not your keys, not your coins” in the aftermath of the hack. Instead, these situations involved highly trusted systems employed by diligent users who followed well-established security practices.
The Coldcard and Liquid Network situations are fundamentally different. These exploits, which have led to somewhere near half a billion dollars worth of unauthorized transfers (although much of the funds taken from Liquid have been returned), occurred within the very systems designed to protect users from issues related to the use of a single, third-party custodian, which means they directly threatened a core value proposition of bitcoin itself.
Hardware wallets are widely considered the gold standard for securing digital assets because they store sensitive cryptographic keys on an isolated device disconnected from the internet. However, the Coldcard vulnerability proved that taking personal responsibility for non-custodial storage does not entirely eliminate third-party trust from the equation.
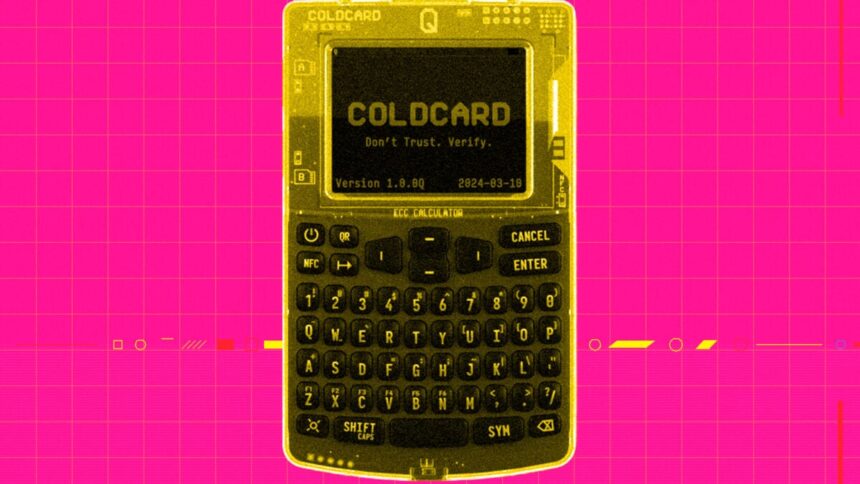
In July, a critical firmware flaw in Coinkite’s popular Coldcard devices shattered the assumption that keys held on specialized, offline hardware are untouchable. A coding error in firmware versions going back to March 2021 bypassed the device’s secure hardware random number generator, relying instead on a more predictable, software-based generator. This flaw allowed remote attackers to brute-force recovery seed phrases generated by the devices and drain over $100 million in bitcoin from thousands of supposedly secure addresses.
This incident serves as a stark reminder of the hidden dependencies that persist even when self-custody wallets are used. For example, users must trust that the device’s hardware is secure, its firmware is free of critical bugs, and no supply-chain tampering occurred during shipping. Relatedly, because purchasing a specialized hardware wallet signals that the owner likely holds significant crypto assets, some bitcoin holders go as far as to argue these devices create an inherent paradox for operational security.
Highly trusted code was once again exposed earlier this month during an exploit of the Liquid Network, which is a federated sidechain designed by Bitcoin technology provider Blockstream that effectively operates on a layer above the base Bitcoin blockchain and is backed by a federation of members using an 11-of-15 multisig wallet. In other words, the system is still custodial but thought to offer a higher degree of security due to the distribution of the associated keys among fifteen parties. To be clear, the federation’s Bitcoin keys were never compromised in the recent security incident.
Instead, a consensus bug in Liquid’s Elements node software allowed an attacker to mint unbacked L-BTC and cash it out via SideSwap for approximately 4,000 bitcoin, worth about $320 million at the time. Vulnerable bridge nodes running the updated Elements software accepted the fake coins as valid, causing the federation’s automated signers to release real bitcoin from the multisig wallet. SideSwap, for their part, also took full responsibility for how the software bug escalated into a permanent loss on the base Bitcoin blockchain. The firm acknowledged that keeping its peg-out authorization key online for automated, same-block payouts, combined with a lack of size, velocity, or origin checks, allowed a 4,000 L-BTC order from a newly created wallet to process without human intervention.
The attackers initially claimed to be white-hat security researchers, initiating on-chain negotiations with Blockstream via OP_RETURN messages on the Bitcoin blockchain. Although the hackers eventually returned 3,400 bitcoin once bridge nodes were patched, they kept 598.5 bitcoin, worth roughly $47 million, from the initial drain. Somewhat heated (and public) discussions between the hackers and Blockstream regarding those remaining funds followed, but the conversation has since gone cold.
The prestige of the company behind Liquid makes the exploit particularly striking. Blockstream was founded in 2014 by some of the most well-respected technical figures associated with Bitcoin, including longtime cypherpunk Adam Back, who was cited in Satoshi Nakamoto’s original Bitcoin whitepaper, and a number of the earliest developers who worked on Bitcoin’s most critical software node and wallet software, known as Bitcoin Core. Despite this background, the flaw was merged into the associated repository on September 1 during an attempt to fix a separate issue.
Frustrated with existing smart contract programming languages? Coming soon to #Elements, #Simplicity enables devs to formally verify the safety, security, & cost of complex smart contracts. Simplicity is so simple it fits on a T-shirt. Available now! 📝🔒 https://t.co/PAVOr208ye pic.twitter.com/v0vnGmR6NL
— Blockstream (@Blockstream) May 31, 2019
Liquid was also designed to be simpler and safer than general-purpose smart-contract platforms like Ethereum or Solana, drawing its original codebase directly from Bitcoin, which has long benefited from a slow, methodical development process and simple, clear functionality. A more advanced programming language developed for Bitcoin and already deployed on Liquid was even named Simplicity.
For many users, the view was that Liquid would inherit much of the security associated with base layer Bitcoin development itself. The Liquid Network has also received significant criticism from purists who did not believe in the federated security model built on top of a multisig address; however, it’s notable that the federated custody model was not the underlying issue at fault here.
To be clear, these failures do not necessarily spell the end of Bitcoin as a technology or its associated crypto asset. But they do require self-custody advocates to dramatically rethink their strategies. For those committed to maintaining sovereign control without relying on a single vendor, multisig configurations across hardware from multiple manufacturers represent a path forward. Collaborative custody platforms like Casa and Unchained offer another alternative where users can secure their assets with the assistance of specialists without handing over a controlling level of custody.
Of course, other users may decide to opt out of self-custody entirely by way of a bitcoin ETF, stock in a bitcoin treasury company, or some other custodial bitcoin derivative. There are plenty of scenarios that exist where people may end up having exposure to bitcoin without necessarily knowing or thinking about it too much. Strategy’s STRC and Tether’s USDT products already do this to some degree, for example. More such products could exist in the future in a scenario where bitcoin continues to gain credibility over time as a global, apolitical reserve asset.
That said, this approach remains highly controversial among Bitcoin purists, who warn of systemic custody centralization risks and the historical precedent of government confiscations, such as Executive Order 6102 in 1933.
The old world is dying, and the new world struggles to be born: now is the time of monsters.
— Electrum (@ElectrumWallet) September 7, 2026
The picture for crypto more generally is less clear, as the large numbers of hacks that have taken place in the space combined with the large attack surfaces involved with more complex crypto systems have put into question whether true decentralized finance (DeFi) will stand the test of time. Some blockchain security experts have already warned against using DeFi at all during this “time of monsters.” In April, the crypto industry experienced its worst month on record for exploits, averaging nearly one attack per day.
While attackers are already using AI to find and exploit bugs, many security teams expect the same tools to become a routine part of defensive code review and, over time, to make well-maintained software harder to break. At the end of the day, it also still matters that Bitcoin’s base layer and consensus-critical Bitcoin Core code have not been successfully exploited in this wave of AI-powered attacks.
Read the full article here